
ESET
Researchers Discover First-Ever Ransomware Misusing Android Accessibility
Services
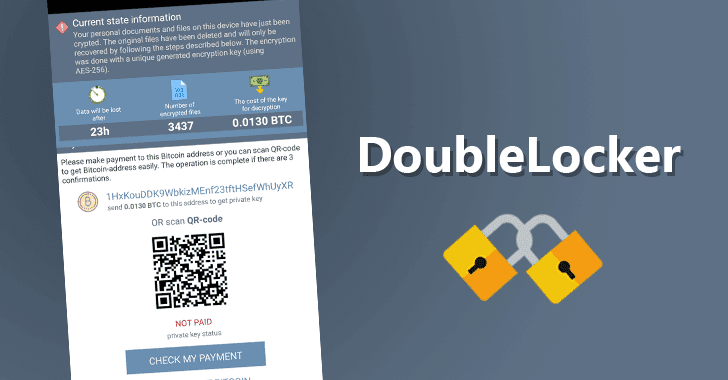
ESET researchers have
discovered DoubleLocker, an innovative Android malware that combines a cunning
infection mechanism with two powerful tools for extorting money from its
victims.
“DoubleLocker misuses Android
accessibility services, which is a popular trick among cybercriminals. Its
payload can change the device’s PIN, preventing the victim from accessing their
device and encrypts the victim’s data. Such a combination hasn’t been seen yet
in the Android ecosystem,” comments Lukáš Štefanko, ESET Malware Researcher who
discovered DoubleLocker.
On top of being ransomware, DoubleLocker is based on
the foundations of a particular, already documented banking Trojan. According to Štefanko, the functionality for
harvesting users’ banking credentials and wiping out their accounts can be
added easily.
“The additional functionality will turn
this malware into what can be called ransom-banker,” warns Lukáš
Štefanko, who claims he spotted a test version of such a ransom-banker in the
wild in May 2017.
For more details, read an article on DoubleLocker at ESET’s
official blog, WeLiveSecurity.
For the LATEST tech updates,
FOLLOW us on our Twitter
LIKE us on our FaceBook
SUBSCRIBE to us on our YouTube Channel!