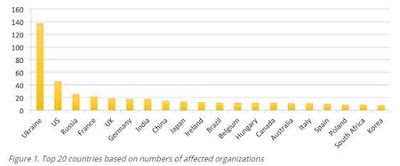
Symantec has confirmed that MEDoc,
a tax and accounting software package, is used for the initial insertion of
Petya into corporate networks. MEDoc
is accounting software that is widely used in the Ukraine, indicating that
organizations in that country were the primary target. After gaining an initial foothold,
Petya then uses a variety of methods to spread across corporate networks.
Petya is a worm, meaning it
has the ability to self-propagate. It does this by building a list of target
computers and using two methods to spread to those computers.
·
Lateral movement:
o
Execution
across network shares: It attempts to spread to the target
computers by copying itself to [COMPUTER NAME]\admin$ using the acquired
credentials. It is then executed remotely using either PsExec or the Windows
Management Instrumentation Command-line (WMIC) tool. Both are legitimate tools.
o
SMB
exploits: It attempts to spread using variations
of the EternalBlue and EternalRomance exploits.
·
Petya
builds a list of IP addresses to spread to, which includes primarily addresses
on the local area network (LAN) but also remote IPs. Once the list of
target computers has been identified, Petya builds out a list of user names and
passwords it can use to spread to those targets. The list of user names and
passwords is stored in memory.
- Initial
infection:
- Petya is initially executed via rundll32.exe using the following command: rundll32.exe perfc.dat, #1
- Once the DLL has been loaded, it will first attempt to remove itself from the infected system. This is done by opening the file and overwriting its contents with null bytes before finally deleting the file from disk. Overwriting the file with null bytes is used as an attempt to thwart recovery of the file using forensic techniques.
- MBR
infection and encryption:
- Once installed, Petya proceeds to modify the master boot record (MBR). This allows it to hijack the normal loading process of the infected computer during the next system reboot. The modified MBR is used to encrypt the hard disk while simulating a CHKDSK screen. It then displays a ransom note to the user.
- Full blog post here.
Petya outbreak: What’s the motive behind this
major cyber attack?
- Sometimes the obvious answer is the right one:
-
- The person or persons behind the attack were technically capable and were attempting to compromise a choice group of financial targets that may be more likely to pay a ransom, as they would need to regain access to important financial records.
- The attacker may not be a particularly smart criminal, however, as using a single bitcoin wallet, and a single e-mail account for contact, was not the best way to get payment.
- The e-mail account was rapidly suspended by its provider, thus disabling the ability of the attacker to interact with victims.
- There
may be a more nefarious motive behind the attack, that is, disruption:
- Similar to Killdisk, perhaps this attack was never intended to make money, rather to simply disrupt a large number of organizations. Launching an attack that would wipe victim hard drives would achieve the same effect, however, that would be an overtly aggressive action. Effectively wiping hard drives through the pretense of ransomware confuses the issue, leaving victims and investigators to ask: “Are the attackers politically motivated, or criminally motivated?”
- Based on the current data, the motive behind the Petya attacks may be the second option. This attack was an ineffective way to make money, but a very effective way to disrupt victims, and sow confusion.